Everything you need to say yes.
Your employee wants to use PurposeMapped. You need to know where the data goes, what the providers do with it, and who at PurposeMapped can touch it. Here is all of that, in writing.
The three facts that matter most
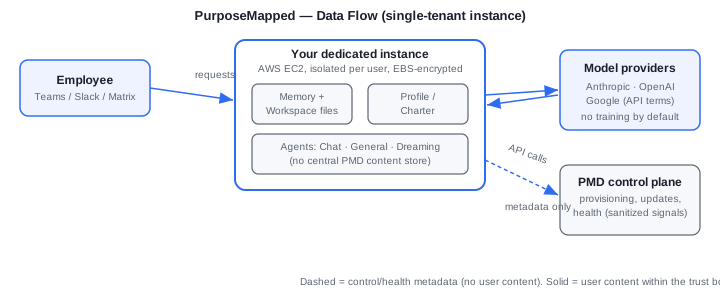
Memory and files live on infrastructure assigned to that one user. No multi-tenant store, no cross-user aggregation, no data monetization.
No training by default; short abuse-monitoring retention windows. Equal to enterprise-tier privacy at the model layer — we say equal, not better.
Support access is consent-based and logged. A user-visible Access Ledger is targeted for Q4 2026 and is not live yet — we won't claim otherwise. Full detail: our privacy policy.
Where a message actually goes
The IT Approval Packet
Three documents covering the technical and policy answers a security review needs.
Individual Use Declaration
One-page summary: what PurposeMapped is, what it accesses, and the operator-access policy.
Security Brief
Encryption, data residency, retention windows, subprocessors, and incident response.
Have a security questionnaire?
Send it over and we'll answer it directly, point by point.
Request our security questionnaire responses